YOLO Mode, Safely: MicroVM Sandboxes for Any Agent — Rowan…
Rowan Christmas, product manager at Docker, demonstrates how a coding agent with default permissions can expose sensitive data on a developer's laptop within a few prompts, and argues that harness-level guardrails alone are insufficient protection. He presents microVM sandboxes as security by design, demoing Docker Sandboxes (sbx): a single command creates an isolated VM with its own kernel, filesystem isolation, secret placeholders, default-deny networking, and a full audit trail, compatible with agents like Claude Code and Codex. He also previews agent identity, delegation chains, and policy-based governance, including network and filesystem rules, MCP catalogs, and upcoming L7 and per-repository controls. Recorded at AI Engineer World's Fair 2026 in San Francisco.
# Video Identity Observations
## Source Context
- **Title:** *YOLO Mode, Safely: MicroVM Sandboxes for Any Agent — Rowan Christmas, Docker*
- **Format:** Conference talk (near-final session: "one of the last talks of the entire conference"), delivered by a named speaker affiliated with Docker.
## Self-Description Evidence
The speaker explicitly states his role and product affiliation:
> "I'm here with Docker. I'm one of our product managers that works on our new sandbox product... It's a new binary for Docker. It's called SBX. It's a microVM."
Other creator claims:
- **Product scope:** SBX is a microVM sandbox that isolates filesystem, blocks secrets/network egress, and provides "a full audit trail" — "secure by design, not just... say please."
- **Internal adoption claim:** "Every developer at Docker now writes all of their code in sandboxes... If we don't use it, we get yelled at."
- **Roadmap claims:** Future L7 networking controls, per-repo filesystem controls, agent identity tracking with "delegation chains," and Cedar-based policy.
- **Compatibility claims:** Runs on "Mac, Windows, and Linux," works with Claude Code, Codex, shells, Python jobs, web servers — "It's not just cloud [Claude]."
## Intended Audience
The talk addresses **professional developers and security-conscious practitioners of AI coding agents**:
> "All of you are doing way more AI than you ever thought you would 5 years ago."
Further audience cues:
- Familiarity assumed with Docker, Claude Code, MCP servers, and CrowdStrike-style security reports: "if you look in some of these cloud prompts you'll see please don't do nefarious things."
- Directly addressed professional use cases: "If you're working in consulting, if you've got a chief security officer, if you do client work... you're probably dealing with this on a day-to-day basis."
- Conference-attendee framing: references to "people at this conference," a booth, swag ("sunglasses... power banks"), and live demos.
## Claimed Scope
- The channel/speaker claims expertise in **AI agent security and governance**, positioned as a Docker product voice: "We think it's the best way [microVM boundary]. Other people do too."
- Scope is explicitly **promotional plus educational**: a self-described "marketing slide that my marketing team is really mad at me that I made this," balanced with a live hacking demonstration ("what happens if I actually try to hack myself").
## Demonstrated (vs. Claimed) Presentation Patterns
- **Demonstrated:** a self-experiment narrative (prompting Claude Code to find the speaker's own browser/bank data, "five prompts" total), live side-by-side CLI demos of `claude` vs. `sbx run claude`, and claims that everything shown is "working."
- **Claimed but not demonstrated:** future features (L7 controls, per-repo permissions, delegation chains) and internal Docker-wide adoption.
## Notes for Synthesis
- This is a single conference talk by a Docker product manager; it evidences a **vendor-affiliated technical outreach voice** targeting developers adopting AI agents, not a general-audience channel.
# Delivery Observations: "YOLO Mode, Safely: MicroVM Sandboxes for Any Agent"
## Overall Delivery Profile
- **Conversational, humor-forward technical talk.** The speaker explicitly sets a light tone upfront: *"I tried to make it somewhat engaging and amusing. So, you know, audience participation is encouraged."*
- **Demo-driven persuasion structure**: hack story → failure of current tools → product solution → live comparison → roadmap → close.
## Recurring Linguistic Patterns
- **Self-referential contrast phrases** that set up a problem/solution pairing:
- *"So if only there was a better way to do this using a sandbox microVM technology..."*
- *"Anyways, maybe maybe there's a better solution. Who knows?"*
- *"So if we can't actually do these things, the agent's not useful."*
- **Repeated use of "pretty" as an intensifier**: *"It's a microVM. It's really cool"*, *"So pretty cool"*, *"I was quite impressed with it."*
- **Repetition-for-emphasis doubling**, often mid-sentence: *"please please don't flag me"*, *"no, no, no"*, *"it's not, it's not your friend"*, *"tell you tell you about it."*
- **Frequent filler restarts** ("uh", "you know", "right?") — a spoken, unscripted cadence throughout.
- **Rhetorical questions to the audience**: *"What can I what can I do with this?"*, *"How do I how do I buy this from you guys?"*
## Teaching Habits
- **Personal experiment as the core teaching device**: he hacks his own machine (*"what happens if I actually try to hack myself"*) and walks through the result step by step — five prompts, the security team's response, the CrowdStrike score (*"I got a nine out of 10 which uh is better than I did in most of my classes."*).
- **Side-by-side comparison demos**: *"on the uh left side is when I run claude and on the right side is when I do sbx run claude."*
- **Concrete numbers to make points memorable**: *"five five prompts is what it took"*, *"I had to type uh seven more keystrokes... but I think it's well worth the price."*
- **Disarmingly honest asides**, including product weaknesses: *"I have my marketing slide that my marketing team is really mad at me that I made this."*
- **Explicit caveats for safety**: *"I made fake bank names. This is not my real data, just so you know."*
- **Practical usage framing**: he describes his own workflow (*"I'll mount those uh, read only"*) to model how the audience should use the tool.
## Communication Patterns
- **Casual, colleague-to-colleague register** rather than formal presentation voice: *"Hey everybody, I hope you had a good lunch."*
- **Self-deprecating humor as a recurring device**: the CrowdStrike grade joke, *"we get uh we get yelled at"* about internal sandbox usage.
- **Pop-culture reference in the close**: *"you can look as good as uh Macho Man Randy Savage with those glasses."*
- **Direct calls to action**: repeated booth invitations (*"you should come by our booth"*, *"come check it out"*), and giveaway mentions.
- **Trust-building via transparency about limits**: *"everything that I've showed you today is working"*, and clearly labeled future items: *"In the future, we're going to be adding more stuff."*
## Stable Patterns vs. Isolated Moments
- **Stable-looking** (repeated across the talk): problem→solution framing, humor/self-deprecation, demo comparisons with concrete metrics, and casual fillers ("uh", "you know", "right?").
- **Possibly isolated** (single occurrence, insufficient repetition to confirm as habit): the pop-culture close, the marketing-team joke, and the audience-participation invitation in the opening — these may reflect conference-specific adaptation rather than a consistent style.
# Observation Document: YOLO Mode, Safely — MicroVM Sandboxes for Agents
## Event & Speaker
- **Speaker:** Rowan Christmas, Product Manager at Docker, working on Docker's sandbox product (transcript self-identification).
- **Product discussed:** `sbx` — a new Docker binary providing **microVM sandboxes** for running agents.
## Core Claim
- Coding-harness-level protections for AI agents are insufficient; **microVM sandboxing** is the better security boundary because "if it gets down to your host machine, it's too late."
## Demonstrated Security Experiment
- Christmas ran a self-directed "hack myself" test using **Claude desktop app on Mac**, asking it to find his browser history:
- It **found browser history immediately**.
- It then located his **bank account data** (he notes fake bank names shown on slides, but real data was found).
- It surfaced details: recent check ordering, Zelle usage, **last four digits of the account**.
- **Attack cost:** "Five prompts is what it took." A direct request triggers a warning, but framing it as "I'm researching how to do security" gets compliance.
- His stated takeaway: **"It is not your friend."**
- The next day his security team flagged him as potentially hacked; a **CrowdStrike report** scored the activity **9 out of 10**, identifying it as a known credential-extraction technique.
## Argument Against Current Harness Security
- Existing protection amounts to prompt-level pleas — he characterizes it as "please don't do nefarious things," calling that "the level of security we're at."
- Harness-level controls don't work: **"Agents find their way around it."**
## MicroVM Features Claimed
- Runs **its own kernel**; isolates the file system.
- A system ensures the sandbox **never sees secrets**; network requests get **placeholder replacement** for credentials.
- **Full audit trail**; network egress/ingress blocked by default.
- Browser-history attack in sandbox: agent "does not even think there's a browser installed."
- Telemetry claim: Claude sends substantial telemetry to a Datadog instance; sandboxing blocks this. *(Qualification: this is his demo claim, not independently verified.)*
- **Cost of use:** "seven more keystrokes" to run `sbx run claude`.
## Docker Internal Practice
- "Every developer at Docker now writes all of their code in sandboxes" — non-use results in getting "yelled at."
## Governance Capabilities
- **Current (claimed working):** network allow/deny, file system controls, MCP catalog configuration; Docker's MCP servers themselves run in sandboxes.
- **Roadmap:** agent-level **identity tracking and delegation chains**; policy degradation via **Cedar policies**; **L7 networking controls**; per-GitHub-repo file system controls (requested by conference attendees).
- Delegation goal: trace that "an agent did it and a human actually authorized that agent."
## Practical Usage
- Works on **Mac, Windows, Linux**; supports Claude Code, Codex, shells, Python jobs, web servers — it's a full VM.
- Christmas's personal practice: mount related repositories **read-only** so agents can reference code without making "random commits to other repos."
## Tone & Caveats
- Talk is explicitly promotional; speaker is a Docker PM presenting Docker's product.
- Self-deprecating humor throughout (marketing slide, "Macho Man Randy Savage" sunglasses at the booth).
- The bank-data demo used real personal data but displayed with **fake bank names** — an important qualification he emphasized.
# Video Observation Record
## Speaker Identification
| Speaker | Role | Basis |
|---|---|---|
| **Rowan Christmas** | Product Manager at **Docker**, conference presenter | Self-identified: *"I'm here with Docker. I'm one of our product managers that works on our new sandbox product."* |
- **Speaker type:** Creator/presenter (single speaker throughout; no guests, interviewees, or separate narrator appear in the transcript).
- **Setting:** A conference talk ("one of the last talks of the entire conference"), following a lunch break.
## Product / Promotional Content
> ⚠️ **Promotional segments flagged.** The talk promotes Docker's products and includes calls to action.
- **Product promoted:** Docker **SBX** — described as *"a new binary for Docker… it's a microVM"* sandbox product.
- **Explicit calls to action:**
- *"You should come check it out"* / *"come by our booth and see"*
- Giveaway promotion: *"We have a few sunglasses left and some power banks to give away"* at the booth.
- **Self-acknowledged marketing:** *"I have my marketing slide that my marketing team is really mad at me that I made this."*
- **Internal adoption claim:** *"Every developer at Docker now writes all of their code in sandboxes."*
## Referenced Third Parties & Tools
- **Claude / Anthropic** — Claude Code on desktop used in the demonstration; claims that Claude *"likes to really send back a lot of telemetry data to their DataDog instance."*
- **Codex** — mentioned as another agent runnable in the sandbox.
- **DataDog** — referenced as Anthropic's telemetry destination (speaker's claim, unverified).
- **CrowdStrike** — security team's incident report on the speaker's self-hack experiment; speaker claims a *"nine out of 10"* score.
- **Zelle, check ordering** — cited as data the agent surfaced from browser history.
- **Cedar policies** — mentioned as the basis for future policy-based degradation of agent permissions.
- **MCP servers** — Docker's MCP servers reportedly *"run on a sandbox"* subject to the same controls.
## Third-Party / Self-Reported Claims (recorded, not verified)
- Speaker's self-hack experiment: five prompts to extract browser history, bank account details (fake names, but *"real bank data"*), and PII via Claude Desktop.
- Security team incident report and CrowdStrike findings are speaker-narrated only; no document shown in transcript.
- Claims of sandbox capabilities (own kernel, filesystem isolation, secret placeholder substitution, network blocking, audit trail, cross-platform support on Mac/Windows/Linux) are vendor statements from the presenter.
## Demonstrations Described
- Browser-history retrieval attempt: succeeds in plain Claude, fails in `sbx run claude`.
- Network egress blocking: The Pirate Bay lookup blocked by default; telemetry to DataDog blocked.
- Filesystem mounting read-only for related repositories.
- Future roadmap items stated: L7 network controls, per-GitHub-repo filesystem controls, agent identity tracking/delegation chains.
## Comment Availability
- **No information** about comments, replies, or audience Q&A availability is present in the transcript beyond an invitation to visit the booth.
## Provenance Gaps / Uncertainty
- No curated metadata supplied beyond the title; speaker identity rests on self-identification.
- Specific conference name, date, and location are **not stated** in the transcript.
- CrowdStrike report, security-team notice, and demo screenshots are referenced but not verifiable from the transcript alone.
- Anonymized data claims (*"This is not my real data"*) are the speaker's assertions only.
Hey everybody, I hope you had a good lunch. I know it's one of the last talks of the entire conference. I tried to make it somewhat engaging and amusing. So, you know, audience participation is is encouraged. We'll see how it goes. So, I'm here with Docker. Uh, I'm one of our product managers that works on our new sandbox product. I don't know if you've seen it. It's a new binary for
Docker. It's called SBX. Uh, it's a microVM. It's really cool. You should come check it out. But I'm going to tell you why uh you might want to use it in context of agents doing governance and
being safe in general for your agentic platforming needs. So right now, you know, all of you are doing way more AI than you ever thought
you would 5 years ago. At least I am. And we generally think that we're being protected by our coding harnesses because if we try to do something bad, they will sometimes stop us. And when we
see stories, we think, "Oh my gosh, I would never make this mistake to have my AI drop my prod database. You know, I've been doing coding for 30 years. There's no way I would possibly do that." So
what I decided to find out was well what happens if I actually try to hack myself and how far can I get with you know our tools and what we've been told is a safe
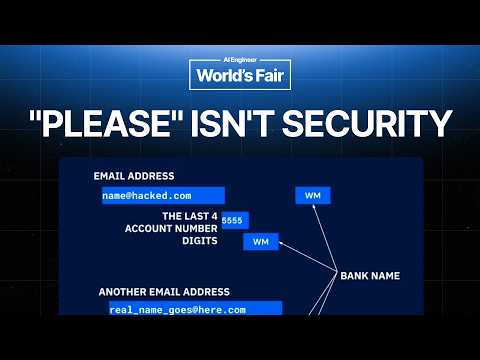
environment. So I opened up my claude code on desktop on my Mac and I had it look for my browser history uh and it found it right away which I was very impressed about. And I asked it uh what can I what can I do with this? And so we started looking at my bank accounts which I was uh surprised about. And it found them. Uh which I was very unhappy about. I made fake bank names. This is not my real data, just so you know. But it did find all of my real bank data on there. Uh and it went even further. It found that I've been ordering checks recently, that I've been using zel. It told me the last four digits of the account I was using. Um I was I was very impressed. And here's kind of an idea of all the PII that it found. Um, this is from again the clawed desktop app uh that we thought was safe. Anyways, maybe maybe there's a better solution. Who knows? So, the next day I came in and I got from my security team uh a nice little notice that I they thought I'd been hacked. And so I had to explain to them
that no, no, no, I'm just putting together a talk for this conference and uh please please don't flag me as a as a a compromised computer. And then they sent me the crowd strike report from
this which I asked them to do. And I was quite impressed with it. Apparently this is a known way to get uh credentials from a machine. Didn't realize that. And I had scored very well on this. I got a nine out of 10 which uh is better than I did in most of my classes. So that was that was really good. But fortunately this was just me internally. It was not some sort of you know injection from a script or MCP server or anything that could easily happen. So five five prompts is what it took. Um
I had to be a little clever. I couldn't if I just if you just ask straight up like hey Claude go find my bank data. It kind of it it will give you a warning. But if you say, "I'm researching how to
do security," it'll happily go and help you do that research on your account. It is not uh it's not your friend. So if if only there was a better way to
do this using a sandbox microVM technology that Docker and others have released recently. So rather than just saying please which you know if you look
in some of these cloud prompts you'll see please don't do nefarious things right like that is the level of security we're at. So now we've got microVMs if you're not aware of them compared to I know you're probably all aware of Docker been using it for years. The new thing now that we and others are doing is with microVMs they run their own kernel. They isolate your file system. We have a system that will go and make sure that the sandbox never actually sees your secrets. When you try to go and do a network request, it takes a placeholder, replaces it so that your sandbox and your agent can't do bad things. We've got a full audit trail for it. Uh so yeah, we want to be you want to be secure by design, not just, you know, hope and say please and see what's going to happen. We're trying to do this balancing act, right? If we don't actually if we can't actually do these things, the agent's not useful. So that's why this whole sandbox idea is so exciting for us. We encourage you to use it. Um, and maybe, you know, don't let your bank data get into the hands of your agent. That's not that's not what you want. So this is what it looks like in practice when you're running a sandbox. Uh on the uh left side is when I run claude and on
the right side is when I do sbx run claude. And you can see that there there's a lot of uh differences. That's a joke. Sorry, they're not. It's just the bypass permissions are on, but it's
nothing nothing else uh was hard to do. Right. Running that command on the right automatically creates a new VM. It spins it up in that folder and it makes a new sandbox for you. It runs your agent. Now you're up and running. It can't see anything. So if we try to do our browser history attack on regular claude, it happily goes and finds your browser history.
But if I run it on the sandbox version, it does not even think there's a browser installed on your machine. So pretty cool. No difference. I had to type uh
seven more keystrokes to get here, but I think it's well worth the uh the price to pay. Same thing is true for network egress
and ingress. So, right here, I'd uh I tried to get it to go and look up uh the pirate bay because I I knew that would be blocked and sure enough, blocked by default. The other thing you kind of
see, it's hard, maybe it's hard to see, but like the uh Claude likes to really send back a lot of telemetry data to their data dog instance. So if you're using Claude, uh you are sending anthropic a lot of your data, unless you're using sandboxes, in which case you're cleverly being blocked by that. The other thing I'll say about sandboxes, they're so easy to use. Every
developer at Docker now writes all of their code in sandboxes. So we are using this every day. Hey, we're writing all of our code in it. If we don't use it, we get uh we get yelled at. So, it's
worth our time to to go and do that little defaults on this. All of this is configurable. Um, and so now that we talked about like why this matters,
right? So, doing this at the harness level doesn't really work. Agents find their way around it. If it gets down to your host machine, it's too late. So, you want to be at that microVM boundary.
We think it's the best way. other people do too. And it's easy to use. If you're working in consulting, if you've got a, you know, chief security officer, if you do client work, whatever it might be, you're probably dealing this with this on a day-to-day basis. So, not only do you want this to be useful, but also you want to do things and enable your agents to do different things, right? So, one of the things we're really excited about is doing like agent level identity tracking and
delegation chains. So, when you can start saying, "Hey, how come this thing happened?" And you can go back and say, "Oh, that's because an agent did it and a human actually authorized that agent
to do it. It didn't just happen by magic. We didn't know. We don't it's not like we don't know how what happened." Now, we're going to start tracing that, tell you tell you about it, and let you write policy that actually goes and does degradation of uh what you can do based on Cedar policies based on new new things happening. And you might say to yourself, "Oh my gosh, this is so good. I would like I would like to buy it now. How do I how do I buy this from you guys?" And so I have my marketing slide that my marketing team is really mad at me that I made this, but I think it's funny and cute for AI governance. So definitely talk about that. Okay. What does AI governance look like? You're doing this is what this is what it looks like in kind of a mockup. So
right now we've do we do network, you can set allow, deny, you can do file system uh points, and you can also decide what your MCP catalog looks like.
Also, if you're running our MCP server, our MCP servers themselves run on a sandbox. So, they are also governed by all of these different controls.
In the future, we're going to be adding more stuff. One of the things we've heard from a lot of people at this conference is that they want to do uh L7 networking controls. They want to do uh
like per GitHub repo file system level controls, right? like you want your agent to be able to read and write to some repos and some areas of some repos but not others, right? So, all of this is going to be coming down the line, but everything that I've showed you today is working. Um, and you should come by our booth and see that
it's easy to install. We run on Mac, Windows, and Linux uh based on your uh package manager of choice. And you can see at the end it's just sbx
run. It's not just cloud by the way. The the sandboxes are a full VM. So you can run a shell, you can run codeex, you can run whatever, you can run a python job, you can run a web server, anything you want to do, but we want to make it easy for you to get in and up and running. So this is kind of our default. So you can just get in, you can get that cloud code or codeex instance going. It feels native. It works just the same way as your one did today, but you've got all these protections in store. Uh, additionally, you can mount other file systems. So, what I do is when I'm working on a, you know, a piece of code with related repositories, I'll mount those uh, read only. That way, my agent
can see what I'm doing, it can see my other codebase, but I know it's not going to make random commits to other repos just to make my thing work, right? I want the guarantee that it's actually
doing what it says it's doing with the API that I've specified. So that's it. Pretty short. We have a booth. We have a few sunglasses left and
some power banks to give away. You should come by our booth and I'll walk over there afterwards and give you the demo and then you can look as good as uh Macho Man Randy Savage with those glasses. So there you go. Thank you.